When your firewall thinks we're a bot
Well, technically our scanner is a bot, but hey... a good one.
The most common wrong answer in uptime monitoring is "your site is down" when the site is fine and the monitor is what got rejected. A Cloudflare challenge page, a WAF returning 403, a hosting firewall dropping our packets -- from the outside these can look like an outage. From the owner's side, everything is up and the scanner is just... unwelcome.
A monitoring service that can't tell the difference is not very useful. So we built the difference in.
How we tell blocked from broken
Several layers, each with its own evidence:
- Fingerprinting. Block pages announce themselves if you look --
cf-rayheaders, Cloudflare challenge markup, Sucuri and Incapsula signatures, mod_security patterns. When a refusal carries a named product fingerprint, we know who said no. - Uniform-refusal heuristic. We ask for a path guaranteed not to exist alongside the real probes. If everything -- real pages and nonsense paths alike -- comes back with the same 403, that's a blanket rule aimed at us, it's not a broken site. A control path that answers differently than the rest tells the opposite story.
- Honest "can't tell". A generic denial with no fingerprint is genuinely ambiguous -- it might be a WAF, it might be a vhost that refuses everyone. We say "appears to be blocking" instead of pretending certainty.
What we deliberately do not do: treat a block as a score. A parked scan isn't a 0/100. It's not a verdict. The site keeps its last real result (if there is one), and the page says plainly why there's nothing newer.
We back off, not hammer
Once a domain blocks us, the dumb move is to retry at full intensity and re-trip the firewall on every cron pass. In Bulgarian we call it "stepping on the same hoe again", and it's something one wouldn't want to do. Instead the domain goes into backoff -- a minimal probe (one connection, one request) until the site starts answering again, with the wait growing exponentially from an hour up to a day. When the site responds normally, the block record clears up and full scans resume on their own. No support ticket required.
What you see
If it's your domain, the evidence shows up in three places:
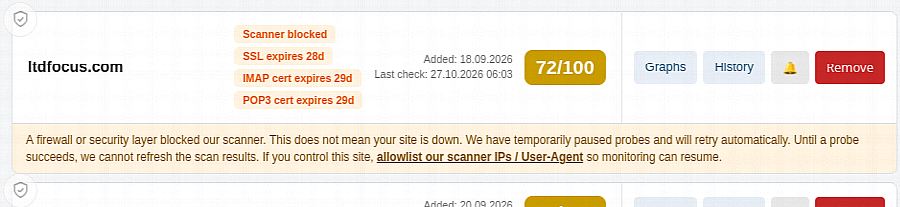
- The scan page: "is blocking our scanner (firewall or bot protection)" with the fingerprint and the reason, over the last usable result -- never a dead-end error page.
- The dashboard: a "Scanner blocked" state, distinct from "down", so a firewall doing its job doesn't page you at 3 AM.
/bot.php: our egress IPs, our User-Agent, and exactly what a scan sends -- everything needed to allowlist us in Cloudflare, your WAF, orrobots.txt/firewall rules.
The uncomfortable truth
Some blocks are simply correct policy -- the owner doesn't want to be scanned, and that's legitimate. The polite-scanner contract means we identify ourselves honestly (dedicated User-Agent, documented IP ranges), respect backoff, and get out of the way. If a site wants us gone, the answer is allowing it to say so -- not getting sneakier.
One last thing -- we have a way to honor an exclusion request. It can be automatic or with our confirmation. It is a way for a site owner to say "Hey, Site is OK, keep off the grass!" and we will listen.
But more about that -- in another blog post.